Source & auditability
You can inspect the desktop client source
Kaption publishes the desktop client as open source. That means the code for screen capture, text recognition, overlay rendering, update checks, crash reporting, local settings, and licence calls can be reviewed instead of guessed at.
Scope matters: the hosted API, production release pipeline, and proprietary translation packs are operated separately by Kaption. The public client repository is for auditing and building the desktop app, not a dump of every service secret or licensed dictionary.
Public scans
VirusTotal results for the current release
Each card opens VirusTotal for that file's SHA-256. The SHA-256 next to each file is what you can hash locally (PowerShell: Get-FileHash .\Kaption-stable-Setup.exe) to prove the file you downloaded matches the one we publish.
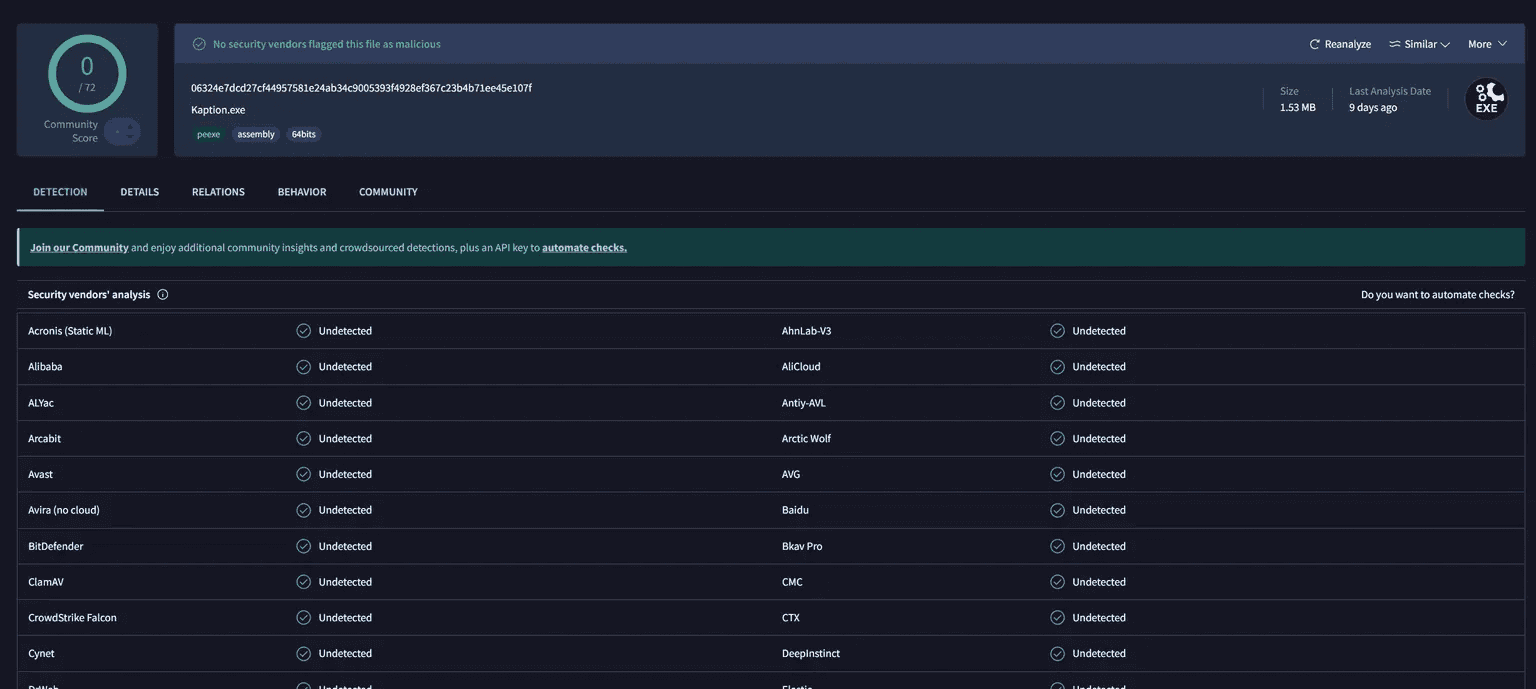
Kaption.exe, 0 / 72 vendors flagged the file.
Kaption 2.5.5, released 2026-11-04. Release on GitHub. Hashes last checked against the GitHub release on 2026-11-04.
In-app updates
Already have Kaption? The app updates itself with Kaption-2.5.5-stable-full.nupkg from our update feed.
SHA-2561507fc1125d3c2914c89655bd0808f8ac9e38f34cdb6b53e5ac00374e7c6c054
Windows SmartScreen
"Windows protected your PC": what's happening
SmartScreen shows "unknown publisher" because the installer is not code-signed during open beta. Authenticode certificates run ~€400/yr, so we are parking that cost until the beta graduates and conversion justifies it.
To proceed: click More info, then Run anyway. This is the standard path for every unsigned indie app. Microsoft Defender itself (the actual antivirus engine behind the prompt) returns a clean scan on the binary. SmartScreen is only evaluating reputation, not threat content.
Heads up: every new release resets the reputation counter. Expect the SmartScreen prompt to re-appear the first time you run a freshly-published version, even after previous builds ran clean.
Heuristic flag
Why Trapmine reports Malicious.moderate.ml.score
Notice the .ml.score suffix. That is not a signature hit against known malware. It is a prediction from a machine-learning classifier. The model has seen features in Kaption's binary that also appear in bad files, so it errs on the side of a warning.
Three of those features apply to us today, and none of them are malicious:
- Unsigned binary. No Authenticode certificate yet (~€400/yr). Every unsigned indie app pays the same penalty with ML-based scanners.
- Low prevalence. Kaption is in open beta. Reputation telemetry has not seen the hash on enough clean machines to mark it as "known good" yet. Every new release resets that counter.
- Installer that extracts nested executables. Our auto-updater (Velopack) ships the app as a compressed package inside Setup.exe and unpacks it on first run. Structurally that is similar to a dropper, even though we are just an installer.
The real signal is the VirusTotal row: Microsoft Defender and ~70 other engines mark the file clean. A proper code-signing certificate is on the roadmap for when the beta graduates. That typically clears the last ML-based heuristic flags too.
Under the hood
What the app actually does on your machine
Does
- Captures a user-picked region of your screen ~10 times per second.
- Runs text recognition locally via ONNX Runtime + DirectML (no cloud).
- Looks up the recognised line in a local translation dictionary.
- Renders a WPF overlay window on top of the game.
- Connects to Kaption's servers (
api.kaption.oneandfiles.kaption.one) to sign in, get translation packs and updates, and confirm the activation about once an hour. Downloads public game text and icons from community hosts (gitlab.com, enka.network, yatta.moe, nanoka.cc).
Does not
- Modify game files, memory, or network traffic.
- Inject DLLs, hook functions, or attach a debugger.
- Upload screenshots or screen images. Recognised text leaves your PC only inside a crash report, and only if you turned crash reports on. The hourly check-in reports how long subtitles were running, which the referral program uses.
- Require administrator rights at runtime.
- Leave background processes after you quit the app.
The full end-user terms are in the EULA. For the data side, see the Privacy Policy.
Still uncomfortable? Want a second pair of eyes before you run it?
Email contact@kaption.one and I'm happy to walk you through what's inside the package. Usually replies within a day.